Items
-
 A discussion about modern disk encryption systems (22c3) Jacob Appelbaum will discuss different disk encryption systems in their current implementation. This will include technical as well as legal issues. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/1112.en.html
-
 The Right Track (22c3) A discussion of the Intellectual Contributions model and the Rights Office system as an alternative for regulating copyright in a digital environment. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/562.en.html
-
 Changing Realities (22c3) The 3D digital world of Second Life has been completely built by its residents. Running on a growing grid of computers, SL's real-time collaborative-creation tools and physical simulation allow for creativity of stunning depth and breadth. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/931.en.html
-
 Syscall proxying fun and applications (22c3) This talk is about how using syscall proxying technique for envolved attacks or other distributed applications. It includes source code examples like shellcodes, tools and a poc rootkit using this technique. This talk will be submited first at 0sec, a private security event we organize in switzerland in october. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/553.en.html
-
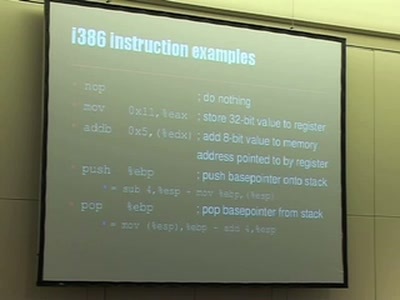 Understanding buffer overflow exploitation (22c3) Everything started with Aleph One's paper "Smashing the Stack for Fun and Profit". These techniques are still the basis for modern exploitation of buffer, heap and format string vulnerabilities. We will give a swift overview about C functions, stack usage, assembler, gcc, gdb and how these few tools can be used to understand and write shell-code to turn simple buffer overflows into backdoors that open whole systems to potential attackers. Sure you want to know how to defend against that. We also will tell you about that! about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/571.en.html
-
 Das Geheimnis - Reloaded (22c3) Seit jeher war es das Gegenteil von Information, ihr dunkler Bruder: das Geheimnis. Jetzt ist es wieder mit aller Macht im Kommen. Peter Glaser über den Weg in die Geheimnisgesellschaft. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/864.en.html
-
 The Web according to W3C (22c3) W3C brings together experts, companies and users to define the fundamental formats and protocols of the Web. The challenge is to create a coherent system (the "Semantic Web") without forgetting everybody's short-term needs. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/429.en.html
-
 Atmel AVR für Dummies (22c3) Mikrocontroller sind heutzutage als Embedded Devices kaum noch wegzudenken. Dieser Workshop soll anhand vom Beispiel fnordlicht[1] zeigen, wie ein Atmel AVR Controller funktioniert und programmiert wird. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/482.en.html
-
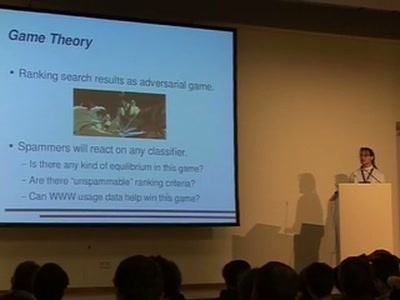 Developing Intelligent Search Engines (22c3) The presentation will give a short overview of the architecture of search engines and how machine learning can help improving search engines. In addition some projects you can take part in will be briefly introduced. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/415.en.html
-
 Die BioP-II-Studie des BSI (22c3) Die BioP-II-Studie sollte eigentlich als Entscheidungshilfe für den Gesetzgeber die Einsatztauglichkeit der biometrischen Merkmale von Finger, Gesicht und Iris in Reisedokumenten testen. Leider wurde ihr Erscheinen um mehrere Monate verzögert und die entsprechenden Gesetze in der Zwischenzeit verabschiedet. Resigniert stellen die Macher der Studie fest, daß sie von der politischen Entscheidung überholt und vor vollendete Tatsachen gestellt wurden. Man hätte lieber auf die Ergebisse warten sollen. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/1094.en.html
-
 We lost the war (22c3) <p>Come to terms with the imminent loss of privacy and civil rights without going lethargic. We will analyse current events, how we think they will affect the issues we care about and how we can be most effective given the new circumstances. Or possibly how to simply survive the times ahead.</p> about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/920.en.html
-
 Literarisches Code-Quartett (22c3) Die Parallelen bei Software und Büchern gehen von dem kreativen Schaffensprozeß über Konsumverhalten, Entlohnung bis zu Fragen wie Lizenzen und Verwertungsmodelle. Wir werden das dieses Jahr noch etwas weiter treiben, indem wir analog zur bekannten Fernsehsendung besonders prägnante Codestücke auf der Bühne mit Publikum kritisieren werden. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/598.en.html
-
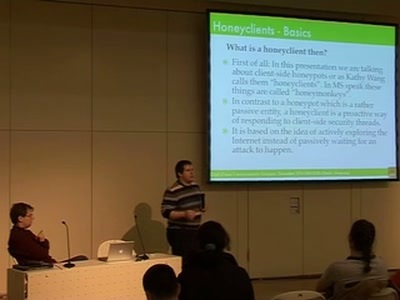 Honeymonkeys (22c3) As part of their ongoing efforts to secure the use of the web for Windows-based systems Microsoft recently launched a new research initiative called Honeymonkeys. This talk will introduce the basic concepts and ideas behind this initiative and will present the speakers' latest research project to gain more knowledge about implementing client-based honeypots. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/871.en.html
-
 Software Patenting (22c3) Patent attorneys and a few large corporations advocate patent law as an appropriate protection tool for software development. Most economists, software professionals and SMEs disagree. They believe patent law does not serve market needs. This year the European Parliament rejected a 'Directive on the patentability of computer-implemented inventions'. However, as the European Patent Offices continues to grant them problems remain. Our expert panel with discuss further developments. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/593.en.html
-
 The Realtime Podcast (22c3) This lecture is more of a live podcast recording session than a traditional talk. So you will be more of an audience in a radio studio while Tim is producing the podcast. In the podcast which is produced in realtime, Tim will lay out the various aspects of podcasting including history, background technology and future directions. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/1147.en.html
-
 Magnetic Stripe Technology (22c3) Find out how magnetic stripe technology works, how it can be hacked, how to build a card reader with parts you can find in your 'junk drawer', and how this reader design can be used to reverse engineer proprietary formats. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/765.en.html
-
 WiFi Long Shots (22c3) What you need to know to successfully design and build a wifi long shot. RF Calculation. Knowledge about the Fresnel Zone. Polarisation of electromagnetic waves. Tricks to avoid interference. Timeout problems of 802.11abg and how to deal with them. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/1078.en.html
-
 I See Airplanes! (22c3) The lecture describes how to build your own passive radar system using relatively low-cost hardware and free software. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/543.en.html
-
 Secure Code (22c3) This talk will introduce new strategies for dealing with entire bug classes, and removing bug attractors from development environments. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/530.en.html
-
 On working memory and mental imagery (22c3) A representation of an untrained human brain, call it B(0), is encoded in the human genome -- its size can hardly exceed a few megabytes. In contrast, a representation of a trained brain, B(t), after big enough time t (say t=20years) must be very long (terabytes?) – it must include a representation of the brain's individual experience. How can a "simple" B(0) change into an extremely complex B(t) in the course of learning? about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/464.en.html
-
 Lightning Talks Day 1 (22c3) There are also loads of reasons for attending the lightning talks (there is a 1-hour block of those each day at 22C3, with 10 talks in a row). It’s entertaining. You get to learn about a lot of different subjects in a short time. And even if one particular speaker is boring: hey, it will be over in just 5 minutes and a new topic will begin. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/911.en.html
-
 Learning cryptography through handcyphers (22c3) For many people cryptography is something that they consider too complicated. But actually one can understand the principles very well if they only try. By looking at old handcyphers used for coding one can begin to understand modern cryptography. about this event: https://hacker-archive.org/assets/22C3/fahrplan/events/469.en.html
-
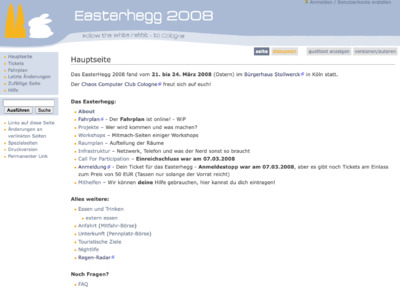 Easterhegg 08 Website Browsable mirror and web archive
-
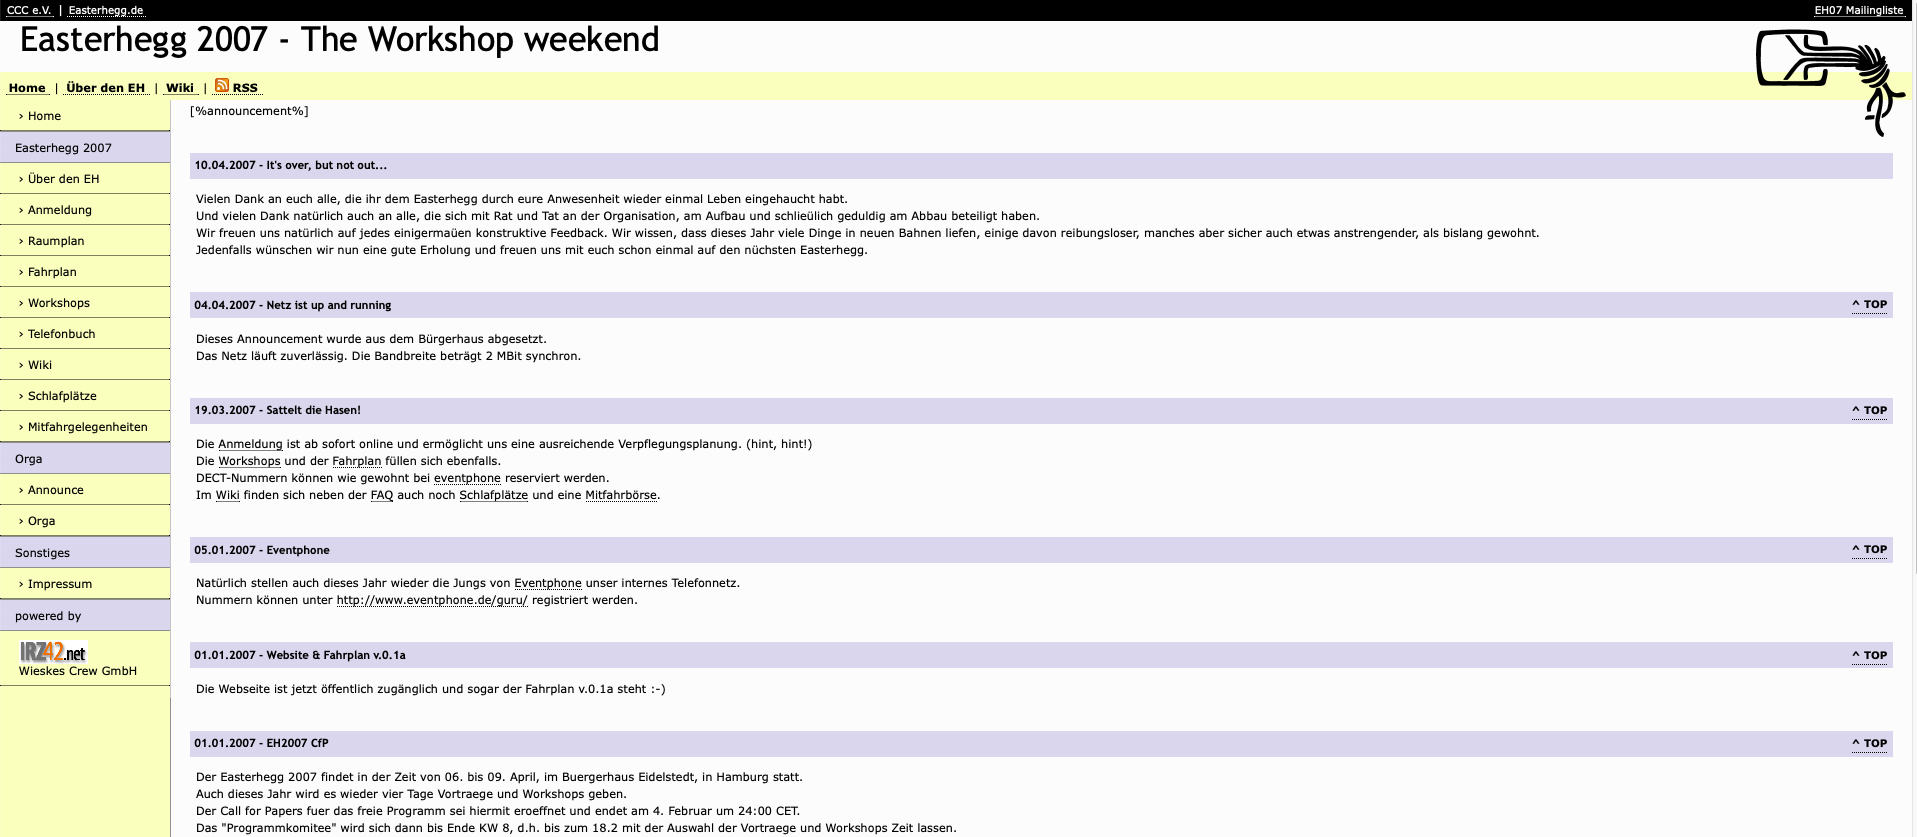 Easterhegg 07 Website Browsable mirror and web archive
-
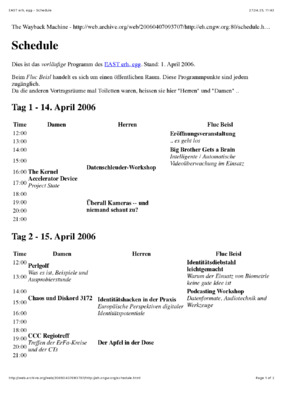 EH06 Fahrplan Fahrplan extrahiert von archive.org
-
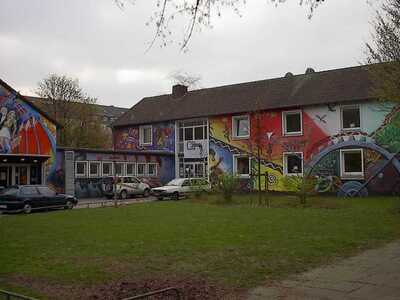 EH02 Photos by Manuel Atug photos taken from atug.de with permission.
-
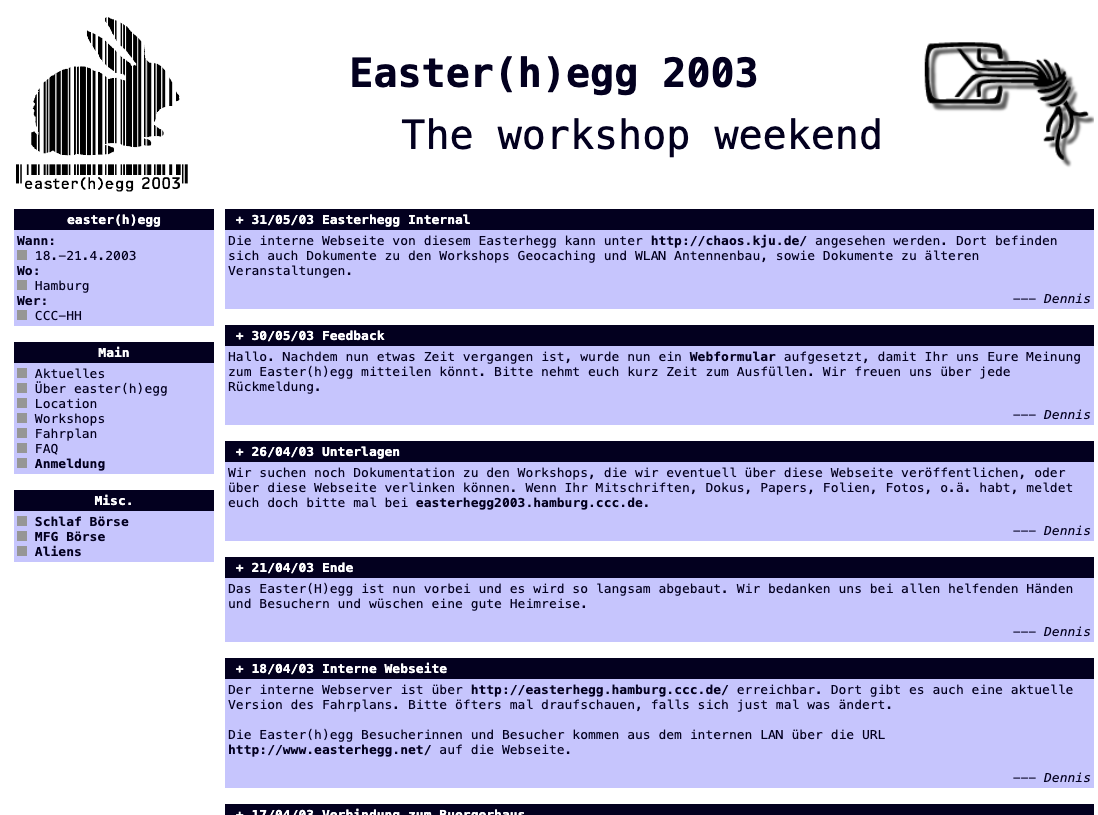 EH03 - Website Browsable mirror and web archive
121–150 of 1565